Bots Are Quietly Working Across the Internet
Every time you use the internet, automated programs are working somewhere in the background. Some help search engines discover new webpages, while others monitor websites, check links, provide online services, organize information, or perform repetitive jobs that would take people an enormous amount of time to complete manually.
These automated workers are commonly called bots. Many are useful and welcome. Others are not. Bad bots can distribute spam, copy information, test stolen login credentials, generate fake traffic, probe websites for weaknesses, and perform other unwanted or malicious activities.
The interesting part is that automation itself is not necessarily good or bad. A bot is essentially software designed to perform a task automatically. What it does, why it exists, who operates it, and how it behaves are what really matter.
That is why simply blocking every bot would be the wrong approach. Website owners generally want legitimate search crawlers to reach the public content they are supposed to see. At the same time, they want to strongly reduce the automated troublemakers constantly looking for opportunities to get somewhere they do not belong.
Think of those bad bots as sneaky little gremlins wandering around the internet checking doors and windows. A perfectly healthy website can still attract them. The challenge is knowing which automated visitors should be welcomed and which ones should be shown the door.
What Is a Bot?
A bot is a software program designed to carry out tasks automatically. Instead of requiring a person to click, search, collect information, check a webpage, submit a request, or repeat the same operation hundreds of times, software can be instructed to perform those actions on its own.
That ability makes automation extremely useful. Consider the size of the internet. It would be impossible for teams of people to manually visit every webpage looking for new or updated information. Automated crawlers can continuously explore the web, discover pages, follow links, and report what they find back to search engines.
The same principle applies to many other jobs. Automated systems can check whether websites are available, monitor services, retrieve permitted information, identify broken links, create webpage previews, and perform countless repetitive tasks.
Unfortunately, the same ability can also be used for harmful purposes. A person could manually try passwords against a login page, copy information from webpages, or inspect websites looking for a particular weakness. A bot can automate those same actions and repeat them across large numbers of targets.
Automation provides the ability. Intent determines how that ability is used.
Good Bots Help Keep the Internet Moving
Good bots perform jobs that website owners and internet users often depend upon without ever seeing them at work. Search engine crawlers are among the most familiar examples.
Googlebot crawls webpages for Google Search, discovering pages, following links, revisiting existing content, and helping Google understand what is available across the web so pages can be considered for its search results. Bingbot performs a similar role for Microsoft Bing. Other legitimate crawlers are associated with search engines and online services such as DuckDuckGo, Baidu, and Yandex.
Good bots are not limited to search engines. Automated systems can monitor whether websites are online, check links, assist security services, create previews when webpages are shared, retrieve permitted public information, and perform many other useful tasks.
For website owners, this creates an important distinction: some bots are visitors you actually want.
Suppose a new article is published. A legitimate search crawler can discover that article, examine its content and links, and return information about the page to its search engine. That process can eventually help someone searching for the subject discover the article. Blocking that crawler unnecessarily would work against the website rather than protect it.
This is why good bot management cannot simply mean block all bots. The objective is to allow legitimate automated visitors to perform useful jobs without giving unwanted automation the same freedom.
The Different Types of Bad Bots
Bad bots take the same speed, repetition, and efficiency that make useful automation possible and apply those advantages to unwanted or malicious activities. Their presence does not automatically mean that a website is poorly maintained or already compromised. A healthy website can still have automated programs knocking on its doors every day.
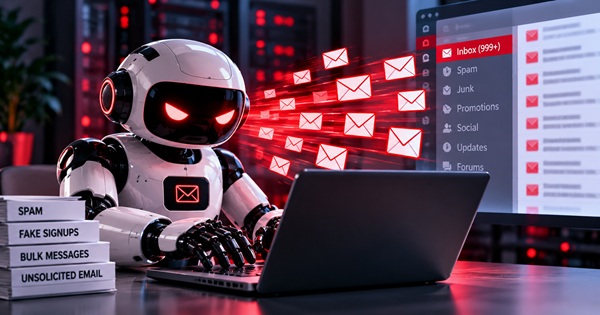
Spam bots automate unwanted messages, fake registrations, form submissions, comments, links, and other forms of spam. A website with an unprotected contact or registration form can quickly discover how persistent automated spam can become.
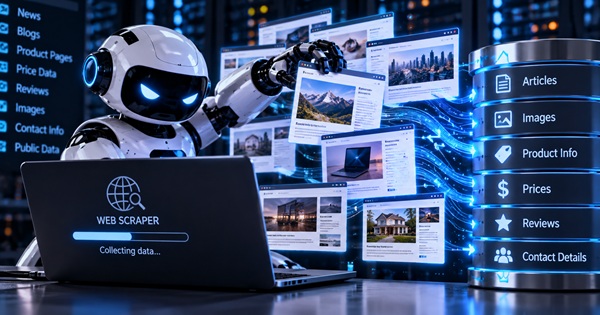
Scraper bots automatically collect information from webpages. Scraping itself is not automatically malicious because search engines, researchers, archives, and legitimate services may retrieve information automatically for valid reasons. Problems arise when scraping becomes unauthorized, excessively aggressive, deceptive, or is used to copy valuable content and information for purposes the website owner never intended.
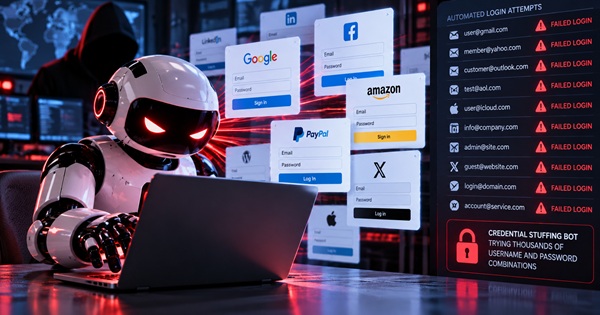
Credential-stuffing bots test usernames and passwords that may have been obtained from previous data breaches. Their strategy depends heavily on password reuse. If someone uses the same email address and password on several services and one suffers a breach, automated attackers may test those credentials elsewhere hoping to find another account that opens.
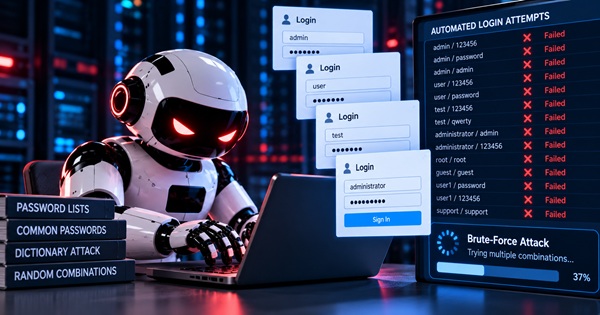
Brute-force bots repeatedly attempt passwords or other login combinations hoping to eventually find one that works, while vulnerability-scanning bots search internet-facing systems for outdated software, exposed services, configuration mistakes, or other weaknesses that could potentially be exploited. Scanning itself can also have legitimate security uses, so once again the intention and authorization behind the activity matter.
Fake-traffic bots create artificial visits, clicks, impressions, or interactions. That activity can contaminate analytics and make it more difficult for a website owner to understand what real visitors are actually doing.
At greater scale, networks of compromised computers and connected devices called botnets can be controlled together. Large botnets may distribute spam, perform attacks, or generate enormous quantities of traffic. When many systems deliberately bombard an online service at the same time, they can contribute to a distributed denial-of-service attack designed to make that service difficult or impossible for legitimate users to reach.
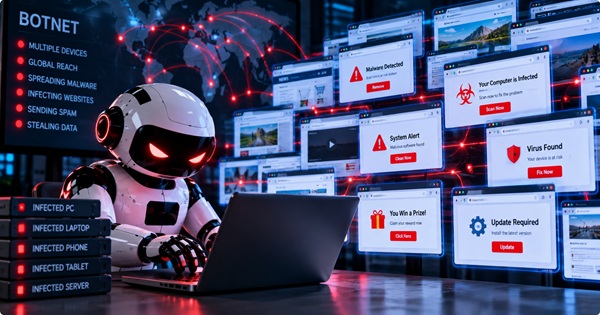
Bad bots can therefore have very different objectives. Some are after information or account access, while others seek copied content, computing resources, money, artificial traffic, or simply disruption.
Why Do Bots Exist?
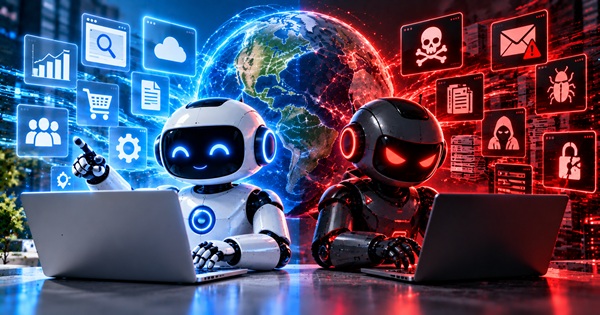
Bots exist largely because the internet has become far too large and active for people to handle every task manually. Search engines need automation to discover and revisit webpages, businesses use it for routine operations, security services use automated systems to monitor activity, and website operators use automation to check performance and availability.
When automation is used responsibly, it can save enormous amounts of time and make online services possible on a scale that manual work simply could not achieve.
But automation does not have a conscience. Software performs the job it has been instructed to perform, which means the same ability to repeat useful tasks quickly can also be attractive to someone who wants to send spam, collect information without permission, test stolen passwords, create artificial traffic, search for vulnerable systems, or disrupt online services.
Good bots automate useful work. Bad bots automate unwanted or harmful work.
The technology can be similar. The purpose is very different.
Why Would Someone Create a Bad Bot?
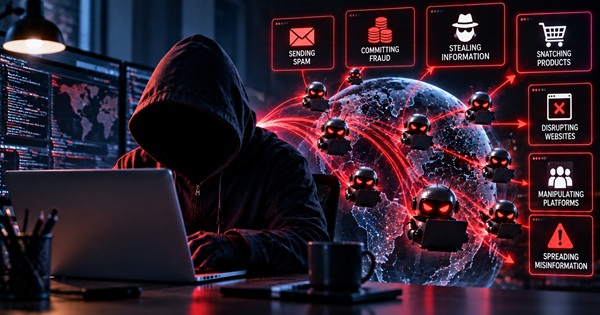
Scaling an attack around a single weakness or vulnerable piece of code explains much of the ruthless attraction.
Imagine someone manually testing a stolen password against one website at a time, and then imagine software performing similar work automatically across large numbers of login pages. The same difference applies to copying information from hundreds of webpages, sending thousands of spam messages, filling forms, or searching websites for a particular weakness.
Automation removes much of the repetitive human effort. Bad bots exist because someone believes there is something to gain from that efficiency. The objective could be money, information, account access, copied content, artificial advertising activity, computing resources, disruption, or information that can be used for another attack later.
Sometimes the bot is only one part of a larger operation. A scanning bot, for example, might merely identify a potential weakness. Another system or person could later decide whether that weakness is worth attempting to exploit.
Bad bots do not necessarily create the weakness they find. They can automate the process of searching for weaknesses that already exist. That is another reason routine website maintenance matters: the fewer useful openings the gremlins find, the less opportunity they have to cause trouble.
Who Is Behind the Good and Bad Bots?
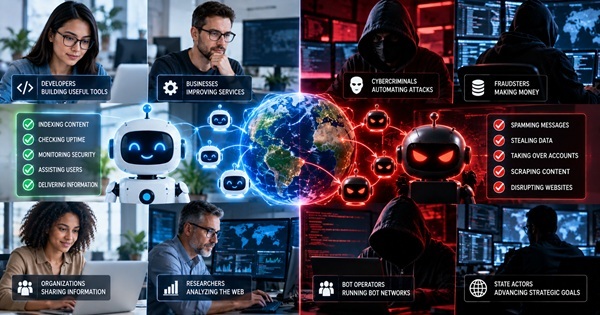
Now we arrive at the who.
There is no single person, company, or organization behind internet bots. Legitimate bots can be operated by search engines, technology companies, security services, website-monitoring services, researchers, online platforms, businesses, and many other organizations performing useful automated work.
Googlebot and Bingbot provide familiar examples because their operators and purposes are known. They are sent out to discover and revisit public webpages as part of operating search engines.
Bad bots are different. Their operators generally have little reason to identify themselves honestly. They may be controlled by spammers, scammers, people attempting to steal account access, operators collecting information without permission, cybercriminals searching for vulnerable systems, or others trying to profit from or disrupt online activity.
That makes the identity of an automated visitor useful when it can be reliably established, but identity alone does not tell the whole story. Website protection increasingly depends upon understanding what an automated visitor is doing, why it appears to be doing it, and whether that behavior should be allowed.
Making a Website Friendly to Good Bots
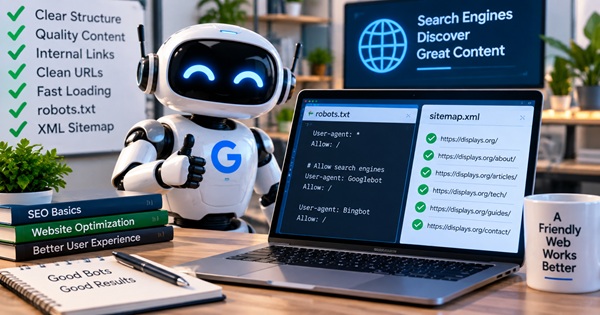
Encouraging good bot activity does not mean trying to attract as many automated visitors as possible. It means making the public portions of a website reasonably accessible to the legitimate crawlers and services that should be able to reach them.
A clear website structure and working internal links help crawlers discover how pages relate to one another. An accurate XML sitemap can provide search engines with useful information about the URLs a website wants them to know about, while a properly configured robots.txt file can provide crawling instructions without accidentally shutting legitimate search crawlers away from important public content.
Reliable hosting and sensible website performance also matter. A website that frequently fails to respond can make crawling more difficult just as it makes browsing frustrating for people.
Security settings deserve attention as well. An overly aggressive firewall rule can occasionally interfere with legitimate automated visitors, so website owners should avoid assuming that every automated request is malicious simply because it did not originate from a person clicking a mouse.
Major search engines also provide webmaster tools that can help site owners understand crawling, indexing, sitemaps, and other search-related issues.
The goal is not simply more bots. The goal is useful automated traffic reaching the content intended for it.
How Websites Recognize Suspicious Bots
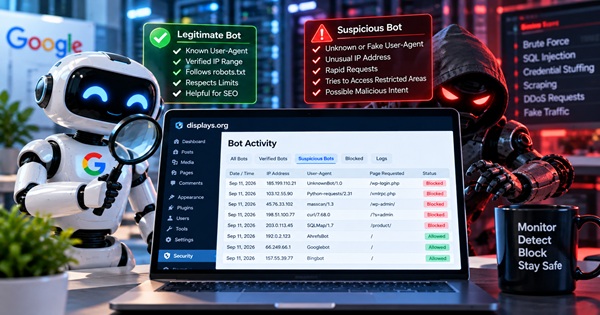
A malicious bot does not usually announce, Hello. I am here to cause trouble. Website protection systems therefore have to look for clues.
One clue can be speed. A normal visitor might read a page for several minutes before opening another one, while automated software may request large numbers of pages or resources in an unusually short period. Repeated behavior can provide another clue. Hundreds of failed login attempts, rapidly repeated form submissions, or requests continually targeting the same sensitive location can look very different from ordinary human browsing.
Where requests originate can matter too. Known abusive networks, suspicious IP addresses, unusual request patterns, and other reputation signals can contribute to a security decision. Modern bot-management and security systems can combine several signals rather than relying on one clue alone.
That matters because legitimate visitors can occasionally behave strangely too. A person rapidly refreshing a page should not automatically be treated like a malicious bot, just as a legitimate search crawler should not be blocked merely because it is automated.
The best response is therefore not always an immediate block. Suspicious activity might be monitored, challenged, slowed through rate limiting, or blocked when the evidence becomes strong enough.
Effective bot management is less like building one enormous wall and more like having an attentive gatekeeper.
How to Strongly Reduce Bad Bot Attacks and Encourage Good Bot Visits
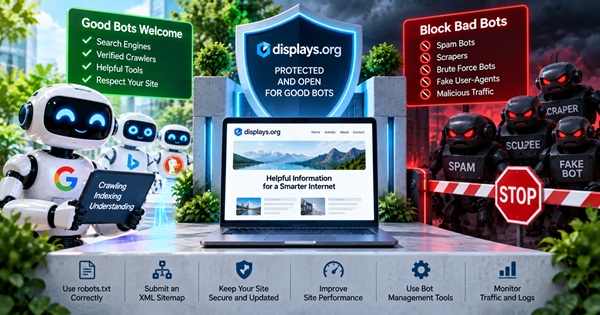
No website owner can press a button and permanently make every bad bot on the internet disappear. The realistic objective is to reduce their opportunities to succeed, and several layers working together can accomplish far more than relying on one security feature alone.
Keep Website Software Updated
Outdated software can provide openings that automated scanners are specifically searching for. WordPress itself, themes, plugins, server software, and other website components should be properly maintained and updated.
Unused components deserve attention too. If an old plugin, theme, account, or service is no longer required, keeping it around can provide another unnecessary area that needs to be protected. A simpler website is not automatically a secure website, but unnecessary doors are rarely useful doors.
Protect Login Areas
Login pages naturally attract automated attention because they protect something valuable: access. Strong, unique passwords make automated password attacks more difficult, while two-factor authentication can add another important layer by requiring something beyond the password itself.
Limiting excessive login attempts and watching for unusual authentication activity can further reduce opportunities for automated attacks. Password reuse should also be avoided because credential-stuffing bots are far less useful when a password exposed somewhere else cannot unlock anything else.
Use CAPTCHA Where It Serves a Purpose
CAPTCHA can help distinguish people from automated submissions around contact forms, registrations, logins, and other areas that commonly attract bots. But more CAPTCHA is not automatically better protection. Placing unnecessary challenges everywhere can frustrate legitimate visitors.
A useful security measure should make life harder for unwanted automation without making the website miserable for the people it was built to serve.
Use a Web Application Firewall and Bot Management
A web application firewall can inspect requests before they reach sensitive parts of a website. Bot-management systems can go further by evaluating automated traffic and deciding whether it appears legitimate, suspicious, or clearly abusive.
Depending on the situation, suspicious traffic can be allowed, monitored, challenged, rate-limited, or blocked. This creates a much more intelligent approach than simply declaring every bot an enemy.
Use Rate Limiting
Speed is one of automation’s greatest advantages. Rate limiting turns that advantage against abusive bots by restricting how frequently certain requests or actions can occur.
A real visitor generally does not need to attempt hundreds of logins within seconds or submit a contact form hundreds of times in rapid succession. Slowing excessive activity can strongly reduce the usefulness of many automated attacks while allowing normal human activity to continue.
Monitor What Is Happening
Security is easier when website owners know what normal traffic looks like. Sudden spikes in requests, repeated failed logins, unusual traffic sources, excessive form submissions, or large changes in server activity can provide clues that something deserves investigation.
Not every unusual event is an attack, but patterns become easier to recognize when someone is paying attention.
Managed Hosting Can Do Much of the Heavy Lifting
Managed hosting can take care of much of the technical work behind running a website, allowing the website owner to concentrate on the website itself. Depending on the provider and hosting plan, this can include server management, maintenance, updates, monitoring, security features, backups, and technical support.
That becomes especially valuable when dealing with automated threats. Website security is rarely provided by one magic switch. Strong protection comes from several layers working together, including properly maintained software, firewalls, bot management, secure accounts, sensible configuration, and reliable hosting.
For many website owners, managed hosting means they do not have to personally manage every technical layer themselves.
You don’t have to become a server expert to take website security seriously.
Keep the Door Open for Legitimate Crawlers
Protection should not accidentally make useful public content invisible. Legitimate search crawlers need reasonable access to webpages intended for public discovery.
That means maintaining internal links, XML sitemaps, appropriate robots.txt instructions, dependable website performance, and sensible firewall settings. Website owners should periodically make sure that important search crawlers are not being unintentionally blocked.
Welcome useful automation. Challenge suspicious automation. Strongly reduce harmful automation.
What Bad Bots Mean for Ordinary Internet Users
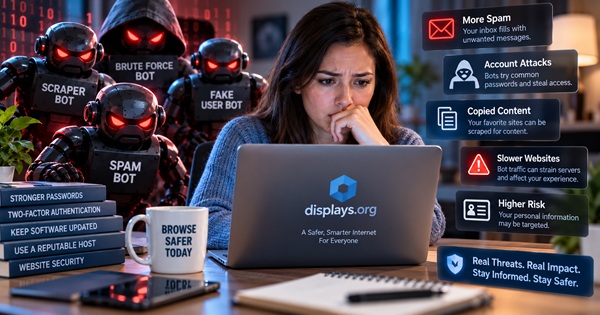
You do not need to own a website to have a reason to care about bots. Many bot-driven attacks ultimately target information belonging to ordinary people, and credential stuffing provides one of the clearest examples.
If login credentials are exposed somewhere and the same password has been reused across several accounts, automated systems can test those credentials against other services. A unique password turns one exposed password into a problem for one account, while a reused password can potentially turn it into a problem for several.
Two-factor authentication provides another layer when a service supports it. Software updates matter on personal devices for much the same reason they matter on websites: known weaknesses are more useful to attackers when they remain uncorrected.
Unexpected login requests, suspicious links, unusual account activity, and requests for sensitive information should also receive appropriate caution.
The technology behind bots can become complicated, but the protective habits do not always have to be. Unique passwords, additional authentication, current software, and careful decisions remain powerful defenses.
Can a VPN Protect You From Bad Bots?
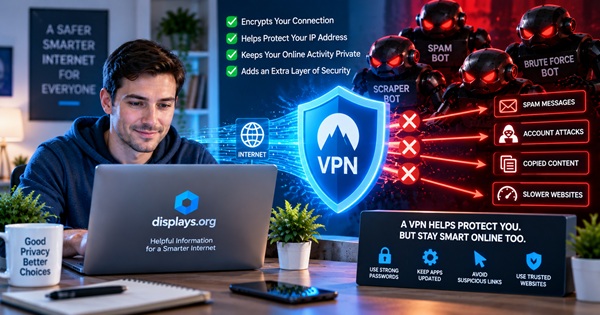
This is an important distinction because VPNs and bot protection solve different problems.
A VPN can encrypt the connection between your device and the VPN server. It can also prevent websites and many online services from seeing your normal public IP address by presenting the VPN server’s address instead. Those are useful privacy and connection protections.
But a VPN does not stop malicious bots from probing a website somewhere else on the internet. It does not replace strong passwords or two-factor authentication, keep WordPress plugins updated, or replace a website firewall or dedicated bot-management system.
Internet security works in layers because different protections perform different jobs. A VPN belongs in that larger picture, but treating it as a universal bad-bot solution would give readers the wrong impression.
Understanding what each security tool actually does makes it easier to decide which protections are appropriate and where they belong.
Humans, Bots and the Growing Role of AI
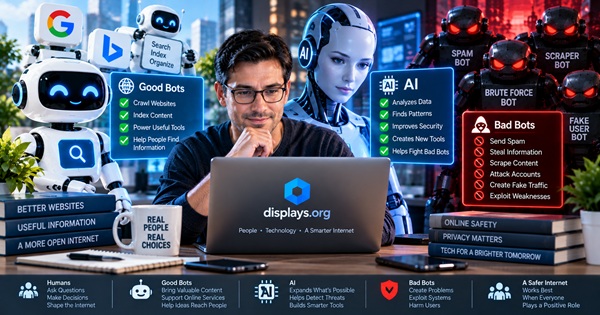
The line between human and automated internet activity is likely to become increasingly interesting as artificial intelligence develops. Bots no longer have to perform only simple repetitive tasks. Automated systems can increasingly analyze information, communicate, make limited decisions, retrieve material, and perform sequences of actions that once required considerably more human involvement.
That does not make every AI-powered bot dangerous. It makes the question of intent and behavior even more important. A useful automated assistant and a malicious automated system might both use sophisticated technology, but their purposes remain entirely different.
Website owners may therefore find themselves asking less often, Is this a bot? and more often:
What is this automated visitor doing, and should I allow it?
That may ultimately become the more useful question.
Good Bots, Bad Bots and Everything Between
Bots are not outsiders waiting to invade the internet. They are already part of how the internet works. Some help search engines discover information, monitor important services, and perform useful repetitive jobs. Others distribute spam, scrape information, probe for weaknesses, test stolen credentials, manufacture fake activity, or participate in larger attacks.
Calling every bot bad would miss half the story. Trusting every bot would miss the other half. The sensible position lies between those extremes.
Understand what automated visitors are doing, understand why they are there, and where possible understand who is operating them. Keep websites maintained, protect important accounts, allow legitimate crawlers to reach the public content they need, challenge suspicious behavior, and strongly reduce harmful automation wherever practical.
And remember our sneaky little gremlins. You may never stop them from walking past the house and checking the door.
But you can make sure they have a very difficult time getting inside.
Additional Recommended Read: Nikola TESLA
Displays.org participates in both the Hosting.com and NordVPN affiliate programs. If you make a purchase through one of our Hosting.com or NordVPN links, Displays.org could receive a commission at no additional cost to you.